
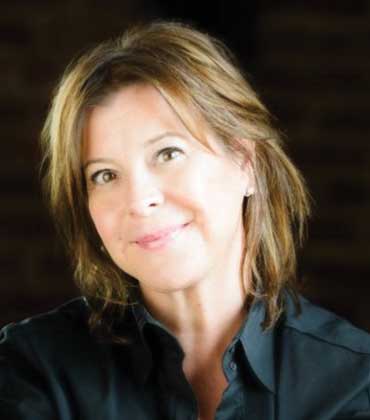
 Beth Murphy, President and CEO
The stakes keep rising. As rules on cybersecurity, data privacy and AI multiply, regulators and boards expect firms to show not only what their policies say, but when they changed, who approved them and who attested to them.
CFM Partners GRC, Inc., a governance, risk and compliance (GRC) technology and intelligence company, has spent more than 25 years helping firms keep that record in one place. For financial services, that work centers on Access Compliance FS, CFM’s GRC solution built on The CFM Network™, which pairs policy management with regulatory monitoring, risk management, audit and education and training.
CFM updates the platform several times a year, guided by a principle that President and CEO Beth Murphy puts plainly: “We work hard to focus our products on the practical application of policy management, particularly in financial services.”
Govern the Policy, Distribute the Manual
That focus shows in how CFM handles a familiar tension. Firms distribute policies as manuals—the compliance manual, supervisory procedures, the code of ethics—but ownership is spread across the firm. The AML officer owns anti-money laundering procedures, trading supervision owns best execution and the chief compliance officer owns the whole.
Built on Financial Services Expertise
CFM's real advantage is deep domain expertise. Institutional broker-dealers, wealth managers, asset managers and independent RIAs answer to different regulatory demands, so CFM builds flexibility into its workflows, audit data and reporting, allowing each to be configured to fit the business and its regulators.
-
We work hard to focus our products on the practical application of policy management, particularly in financial services.
That depth matters even at the largest institutions. At one top-tier bank client, Murphy notes, SEC-regulated units recently resisted moving their policies into an enterprise-wide system because they needed CFM's deeper audit trail.
That audit trail pays off in routine work, too. One longtime client came to CFM with scattered policies and departmental manuals. Today, during the annual compliance review or when an examiner asks how a policy evolved, the client can pull up an earlier version and show what changed, when and why.
Knowing Who Has Seen It
A policy only helps if the right people know about it. Access Compliance FS distributes each policy by role and records when each user views it and, separately, when they attest to it. Compliance teams can see who has not and follow up before an examiner asks.
"You can have the best and most upto-date policies, but if nobody knows about them, it's very hard to then use that as a defense," Murphy says.
When a policy needs more than an attestation, role-based training can be added on the same platform.
From Recordkeeping to Foresight
AI adds a new dimension. AI tools are only as reliable as the policies behind them and the policies that govern AI itself need the same review, approval and attestation trail as any other. CFM's next step is to make better use of the data its clients' processes generate, investing in stronger dashboards, deeper analytics and carefully applied AI to help clients spot where risk may be building before it escalates.
That foresight builds on what CFM delivers today: a single record of how each policy was reviewed, approved, distributed and acknowledged, ready when the examiner asks. That combination earned CFM Partners GRC, Inc. recognition as a Top Policy Management Solutions 2026 honoree from Financial Services Review.
